Spirit Airlines Is Selling Its Workers’ Data. That Can’t Fly.
Abigail Kunkler, Mayu Tobin-Miyaji / Oct 12, 2026Abigail Kunkler and Mayu Tobin-Miyaji are counsels at EPIC.
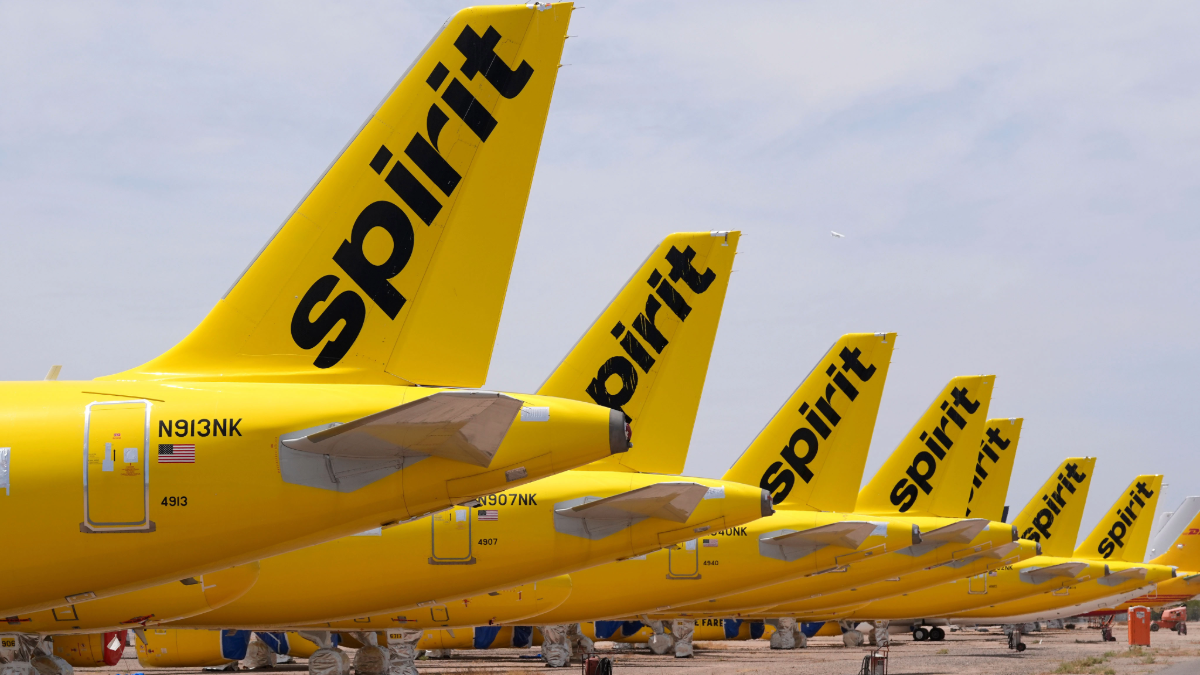
Mothballed Spirit Airlines passenger planes sit parked at Goodyear Airport, Thursday, May 28, 2026, in Goodyear, Ariz. (AP Photo/Ross D. Franklin)
The now-defunct Spirit Airlines is attempting to sell its data, which includes troves of employee data, to Google for $10 million in its bankruptcy proceedings. Google is proposing to purchase this data to train its artificial intelligence systems. While the sale agreement claims that Google is not seeking personal data, the agreement only references consumer data and privacy, with no mention of protecting the privacy of the airline’s employees. This omission displays the parties’ carelessness towards workers’ privacy and threatens to set a dangerous precedent. Shortly after the sale was announced, the Association of Flight Attendants-CWA, AFL-CIO (AFA-CWA) objected to the sale, raising concerns for their members’ privacy.
In light of the privacy issues at stake, EPIC and Professor Seema N. Patel, represented by the Harvard Cyberlaw Clinic, recently submitted an amicus brief to the US bankruptcy court for the Southern District of New York supporting the AFA-CWA's position, laying out the privacy harms and warning the court of the consequences this sale would have for workers. This is an important case for those interested in privacy and worker power to understand the bankruptcy sale at issue, its broader implications, and what must change to protect worker interests moving forward in light of generative AI companies’ insatiable appetite for training data.
Google and Spirit’s data sale agreement is insufficient to protect employee privacy
Former Spirit Airlines employees are justifiably “freaked out” about this sale. The sale agreement’s list of data assets enumerates troves of Spirit employee data. They include employee data going back to 1986; time card information; payroll records; employee tax forms; emails; and Microsoft Teams messages. The disclosure of this dataset presents a serious privacy risk for anyone who has ever worked for Spirit. The employment records contain sensitive information, such as tax and financial information, addresses, contents of internal communications on Teams, and disciplinary and performance records. The disclosure of tax and other financial information can create threats of identity theft. Further, the data may reveal sensitive insights about individual workers—messages may show workers organizing for better pay and working conditions against management; discussions of health conditions or disabilities; or conversations about religion or family life. These types of information can reveal sensitive information that the employee never expected to leave the context in which they were disclosed, risk the employee’s future job prospects, and take away employees’ peace of mind.
While the original sale agreement does not clearly provide for any privacy protections for employee data, the latest filing by the AFA indicates that Spirit has agreed to wholly exclude the most sensitive sets of data, including medical and disability data and drug and alcohol testing records, conceding the privacy interest at stake. There are also ongoing discussions to require the parties to deidentify the rest of employee data, according to the filing. The wholesale exclusion of sensitive data from the sale would be a positive step if the agreement is finalized. However, the deidentification for the rest of the data is not a magic bullet. Depending on how the data is processed, “deidentified” data, analyzed together with other data that relates to the same person, such as data included in emails or other documents, could still lead to reidentification. Further, with increasingly advanced AI systems and a trove of employee data combined with any already publicly available data, individual employees’ attributes could be inferred, leaving employees still vulnerable to privacy risks.
The risk of reidentification presents its own privacy harms. Reidentification by Google or future recipients of data would be a completely unexpected use of their data and robs the affected employees of control over their data. Employees could not have imagined, much less expected, that the data collected for the purpose of performing their job duties would be used to train AI models when they accepted their job offers. Spirit’s sale of employee data that risks reidentification betrays the trust employees put in Spirit when their data was collected to perform their job duties.
The employees also lack the ability to hold Google or Spirit accountable. The sale agreement indicates that Google is solely responsible for nominating the third party to deidentify the data, with no formal role for employees to play in ensuring proper deidentification. Even if Google promises that it and any future recipients of data will not intentionally reidentify employees from the data, as it does in regard to consumer data, as a matter of contract law, the AFA nor the affected employees can enforce that promise. Google would essentially be asking the employees to rely on its pinky promise.
Because of these layered privacy risks, the bankruptcy court must proceed with extreme caution. If this sale is allowed to proceed over the objection of the AFA-CWA and other unions, it would cement the perverse incentives for employers to collect as much data about employees as possible for potential monetization in bankruptcy. This would be an unsettling and dangerous precedent for all workers in the US that would undermine their dignity and power.
The legal landscape that leaves workers unprotected
While Spirit’s attempt to sell its employees’ data is shocking, it was not unpredictable. Decades of widening power imbalances and diminishing legal protections led to this sale. The stakes are high for workers seeking to exercise their rights or bargain with their employer, often prohibitively so; most US workers are at-will, meaning they could be let go for any reason, or for no reason at all. While employers are granted broad control to organize their workplace and workforce as they see fit—including by mandating invasive technology that continuously extracts data from or generates data about workers—workers are left with little ability to challenge new technologies, data collections, or data uses in the workplace. This is particularly true for the majority of US workers who do not belong to a union.
The law has not stepped up to protect worker privacy. Many privacy laws in the US treat data as a property asset, and most exclude workers from data protections. The Bankruptcy Code similarly limits its privacy inquiries to consumers. When workers try to vindicate their limited privacy rights in court, courts rarely grant relief. Taken together, the law views a worker’s information—whether it is collected from, generated by, or inferred about them—as an employer-controlled asset that cannot be infringed upon.
If the court takes seriously the risks to workers’ privacy and livelihoods posed by the sale, it will not allow it to go forward. The Federal Trade Commission and state Attorneys General should intervene to protect the privacy rights of Spirit workers, as they did in other watershed bankruptcies like 23AndMe. Regardless of the court’s decision, however, US policymakers and worker advocates have significant work ahead to dismantle both the incentives to collect and sell worker data and the framework that makes it possible. Adequately addressing the threat Spirit workers now face requires establishing a legal framework that provides meaningful protections for worker privacy and moves away from treating data as the employer’s property to be bought and sold and the workplace as an employer-dominated fiefdom that should be left to regulate itself.
Labor unions should take the sale as a sign to bargain proactively for privacy protections. Spirit’s bankruptcy makes clear what privacy advocates have warned about for years—corporations consider all data, not just consumer data, property to be sold to the highest bidder. The AFA-CWA was the first to object to the sale of employee information and other data that implicates worker privacy. It is a testament to the power of a union that the companies came to the table, stalling the sale for the past two months and negotiating for protections. Although privacy has not historically been a focal point for labor bargaining, this bankruptcy is also a call for unions to prioritize their members’ privacy and digital rights when bargaining with employers. A strong bargaining agreement that dictates what information employers may collect, when, and how they use or disclose that information is key to preventing harms to workers like these in the future.
US lawmakers need to step up to provide solutions for all workers, not just those that belong to a union. There are two key starting places. First, policymakers should update the Bankruptcy Code to provide stronger privacy protections for workers and consumers. Congress did so to protect consumer data in 2005, after Toysmart, an online children’s toy retailer, attempted to sell children’s data in bankruptcy. Congress should do so again for employees’ data. Second, policymakers should create meaningful rights and safeguards for worker privacy. These should include a strong, purpose-based data minimization framework that prohibits employers from collecting information they do not strictly need, limits the permissible uses of the information collected, and bans the sale of employees’ data. These protections effectively curb employers’ incentives to over-collect, abuse, and monetize workers’ data.
Authors