Bugmageddon? Patchpocalypse? Naming the AI Vulnerability Flood
Justin Hendrix, Ashley Faler / Nov 18, 2026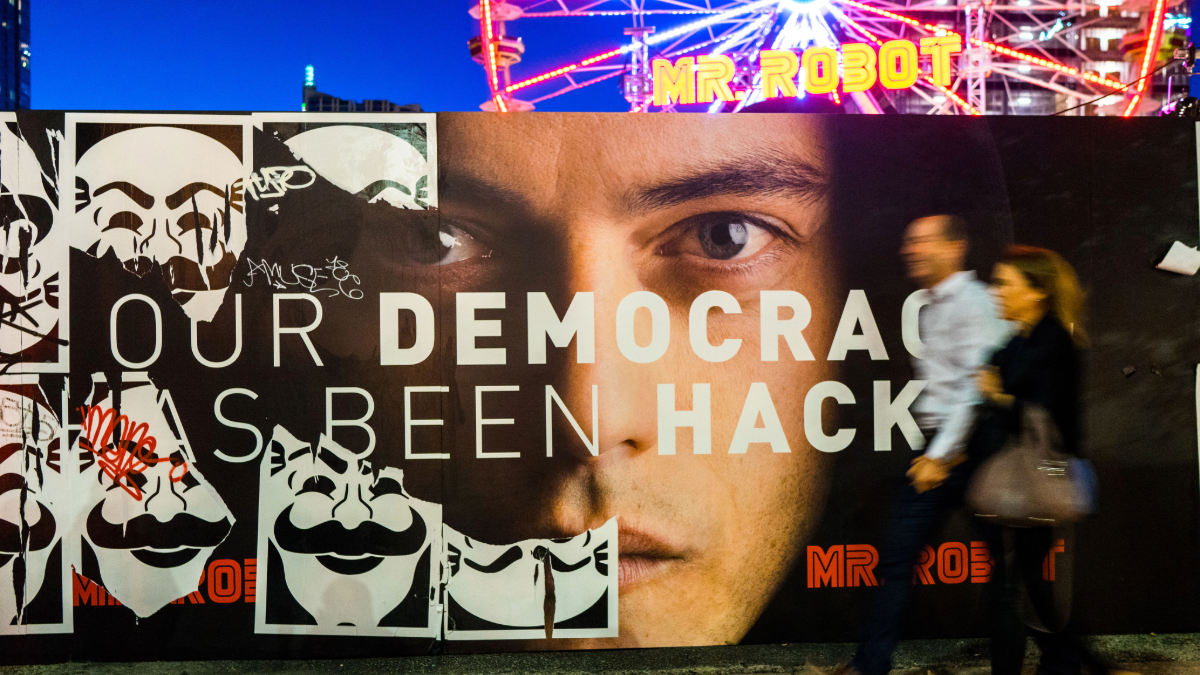
People walk by a carnival event for the USA television show Mr. Robot during SXSW in Austin, Texas in March 2016.
Since Anthropic introduced Claude Mythos Preview in April, AI systems have been finding software flaws faster than companies and governments can fix them. This week saw another big flaw discovered, this time in Java, a programming language The New York Times says is “used by government agencies and about 90 percent of Fortune 500 companies.”
Indeed, the number of publicly disclosed vulnerabilities this year passed 100,000 on Nov. 13, more than double the 2025 total, The Register reported last week. Microsoft fixed a record 622 flaws in a single Patch Tuesday in July. Bank of America brought in 1,000 contractors to patch the bugs Mythos found. And in the past week, outages hit Microsoft, the Federal Aviation Administration, JPMorgan Chase, the National Security Agency and Apple, suggesting that the rush to patch is itself breaking things.
A phenomenon this big needs a catchy name, and many experts, journalists and commentators have offered one.
- Security insiders had been using the term "Vulnpocalypse" for months before Mythos arrived, according to the Cloud Security Alliance's Rich Mogull on April 8.
- The Wall Street Journal went with "Bugmageddon" on April 13.
- The UK's National Cyber Security Centre told organizations to prepare for a "vulnerability patch wave” in May.
- J.P. Morgan's Michael Cembalest chose "Patchmageddon” in July.
- Journalist Nicole Perlroth offered "vulnageddon” yesterday in a post on X.
- A FedWatch chart shared Nov. 18 by CNBC's Carl Quintanilla called it the "Patchpocalypse."
- And Adrian Sanabria, who writes for The Defender's Initiative newsletter, appears to have coined "vulnmaxxing" for the push to find vulnerabilities ever faster.
The names have reached Washington, too. Jack Cable, CEO of the security firm Corridor, told a House Homeland Security subcommittee in June that "to prevent the bugpocalypse, we need a new path forward." At the same hearing, Google Threat Intelligence vice president Sandra Joyce warned in her written testimony of "a deluge of vulnerabilities."
Not everyone in the US government likes the labels. At the Black Hat conference in August, Lindsey Cerkovnik, then a branch chief for vulnerability response at the Cybersecurity and Infrastructure Security Agency, recalled a presenter at a CVE Program listening session saying, "Let's kill the word 'vulnpocalypse,' because it's just not accurate." Cerknovik acknowledged that “Language matters. … It’s harder to take action on a serious threat when you give it a non-serious name and you talk about it in a way that makes it sound like it’s unsolvable.”
Below are the names we have found via search so far, who used them and when. Seen another? Send it to [email protected], or tag us on Bluesky or Instagram.
Naming the flood
What do we call it?
Here is our running tally of terms, newest first, dated by the earliest use we could document and linked to it.
Filter by type
- Nov. 17
Vulnageddon-(ma)geddon
Journalist Nicole Perlroth, on X: "This is collectively being referred to as 'vulnageddon' or 'the vulnpocalypse.'"
- Nov. 17
Software BeirutOther
Journalist Nicole Perlroth, on X: "'Software Beirut' is an incredibly apt analogy."
Perlroth credits the analogy to others; we could not find its source.
- Nov. 14
Vulnerability tsunamiNatural disaster
Anthropic deputy CISO Jason Clinton, on X, reported by The Express: AI chief warns humanity is facing 'tsunami of vulnerability' and says 'it'll get worse'
“The vulnerability tsunami is coming in just a few months, and there won't be enough time to patch critical infrastructure.”
Date is The Express's; we did not see Clinton's post itself.
- Nov. 9
Patch floodNatural disaster
The Register, Simon Sharwood: Linus Torvalds sees signs AI-prompted patch flood has peaked
The plain description, and maybe the good news: Torvalds thinks it has peaked.
- Oct. 23
Black OctoberOther
CNBC, Ashley Capoot: AI's 'Black October': Critical PHP flaws set off global security scramble
Narrower: one bad month. The WSJ credits "cybersecurity pundits."
Also used by WSJ, Nov. 18
- Oct. 15
Summer of HellOther
Cisco Talos, Thorsten Rosendahl: The Q3 Vulnerability Pulse: Discovery ≠ Exploitation
Talos lists it among the phrases the industry picked up this year; we could not find who said it first.
- Oct. 15
Breachpocalypse-pocalypse
Cisco Talos, Thorsten Rosendahl: The Q3 Vulnerability Pulse: Discovery ≠ Exploitation
The feared next act: a wave of actual breaches. Dataminr questions whether it is arriving.
Also used by Dataminr, Oct. 27
- Aug. 11
Patchageddon-(ma)geddon
PDQ, Brock Bingham: Patch Tuesday August 2026
“Last month I declared patchageddon was officially upon us”
Patchmageddon, minus the "m."
- July 22
Patchmageddon-(ma)geddon
J.P. Morgan, Michael Cembalest, Eye on the Market: Patchmageddon
- July 14
Patchpocalypse-pocalypse
The Register, Brandon Vigliarolo: Patchpocalypse Now: Microsoft tops last month's record with 622 Patch Tuesday CVEs
Also used by The Register, Nov. 9; FedWatch via Carl Quintanilla, Nov. 18
- May 29
Vulnerability Apocalypse-pocalypse
Immunefi CEO Mitchell Amador, on his newsletter: The Vulnerability Apocalypse
“The Vulnerability Apocalypse is what happens when the world finds vulnerabilities faster than they can be mitigated.”
- May 26
Vulnerapocalypse-pocalypse
Phoenix Security, Marcus Webb: Vulnerapocalypse — From Vulnerability Discovery to Remediation Speed: Surviving the AI-Driven Patch Wave
- May 6
Bugpocalypse-pocalypse
Risky Business podcast, Patrick Gray, James Wilson and Brad Arkin: Risky Business #836 -- You can't patch the bugpocalypse
The CSA's "Bugpocalypse Threshold" is the point at which AI-found bugs permanently outpace the industry's ability to fix them.
- May 5
Bugocalypse-pocalypse
Alex Stamos of Corridor, quoted in Rest of World: The global cybersecurity gap deepens as AI-powered attacks surge
“It's an AI bugocalypse.”
Same idea as Bugpocalypse, one letter lighter.
- May 4
SlopdemicOther
Bugcrowd founder Casey Ellis, on his blog: Thoughts on the #slopdemic
“So, I'm proposing a new term to pair with #vulnpocalypse: The #slopdemic.”
For the side effect: a flood of low-quality, AI-written bug reports.
- May 1
Vulnerability patch waveNatural disaster
UK National Cyber Security Centre, CTO Ollie Whitehouse: Preparing for a 'vulnerability patch wave'
“This is why we are encouraging all organisations to prepare now for when a 'patch wave' arrives ...”
The government's version.
- April 30
Patch tsunamiNatural disaster
Quest Software, Bastiaan Verdonk: The patching tsunami is here: Fortify identity security against Mythos threats
- April 29
The Mythos momentOther
IBM, Trent Shupe: The Mythos moment: When discovery outpaces defense
- April 29
Patch Apocalypse-pocalypse
Ivanti, Chris Goettl: We're in a Patch Apocalypse. That Means These Three IT Excuses Won't Work Anymore.
Ivanti's page shows only a last-updated date.
Also used by Help Net Security, Aug. 7
- April 22
Vulnerability DelugeNatural disaster
Black Kite, Ferhat Dikbiyik: After Mythos: Are You Ready for the Vulnerability Deluge?
“The Vulnerability Deluge is not a future scenario.”
- April 21
The Mythos effectOther
Syndis: The Mythos effect: Securing your infrastructure against AI-generated exploits
- April 13
CVE avalancheNatural disaster
IONIX, CEO Marc Gaffan: Are You Ready for the CVE Avalanche?
“The CVE avalanche is coming.”
Also used by Daniel Stenberg, Oct. 20
- April 13
Bugmageddon-(ma)geddon
The Wall Street Journal, Robert McMillan and Chip Cutter: AI Is Finding Bugs That Hackers Can Exploit. Get Ready for Bugmageddon.
The Journal's headline coined it; the story itself says "bug armageddon."
- April 12
AI Vulnerability StormNatural disaster
Cloud Security Alliance, SANS Institute and others; Gadi Evron, Rich Mogull and Robert T. Lee: The "AI Vulnerability Storm": Building a "Mythos-ready" Security Program
Also used by FIRST's Chris Gibson, June 15
- April 8
Vulnpocalypse-pocalypse
Cloud Security Alliance, Rich Mogull: Anthropic's Mythos is Here: Defending from the Vulnpocalypse
“I don't really know who coined it, but for the past six months or so we've been tossing around the term 'Vulnpocalypse.'”
The industry's default. Mogull says informal use goes back to about October 2025.
Also used by NBC News, April 11; The Register, May 14; Alex Gaynor, July 15; Trend Micro, July 21; Cisco Talos, Oct. 15; Dataminr, Oct. 27; Nicole Perlroth (X), Nov. 17
How we compiled this. Tech Policy Press searched news coverage, security-industry research and social media for names given to the 2026 surge in AI-discovered software vulnerabilities and patches. Each entry links to a page where we confirmed the term appears; the date is the earliest use we could document, not necessarily the first ever. Research and source checks were done with Anthropic's Claude Opus 5.5, an AI model, with prompts from Tech Policy Press editors, who reviewed the results.
Checked through Nov. 18, 2026.
Authors