AI Governance Needs an Internet-Style Network, Not a Global Overseer
Konstantinos Komaitis / Oct 13, 2026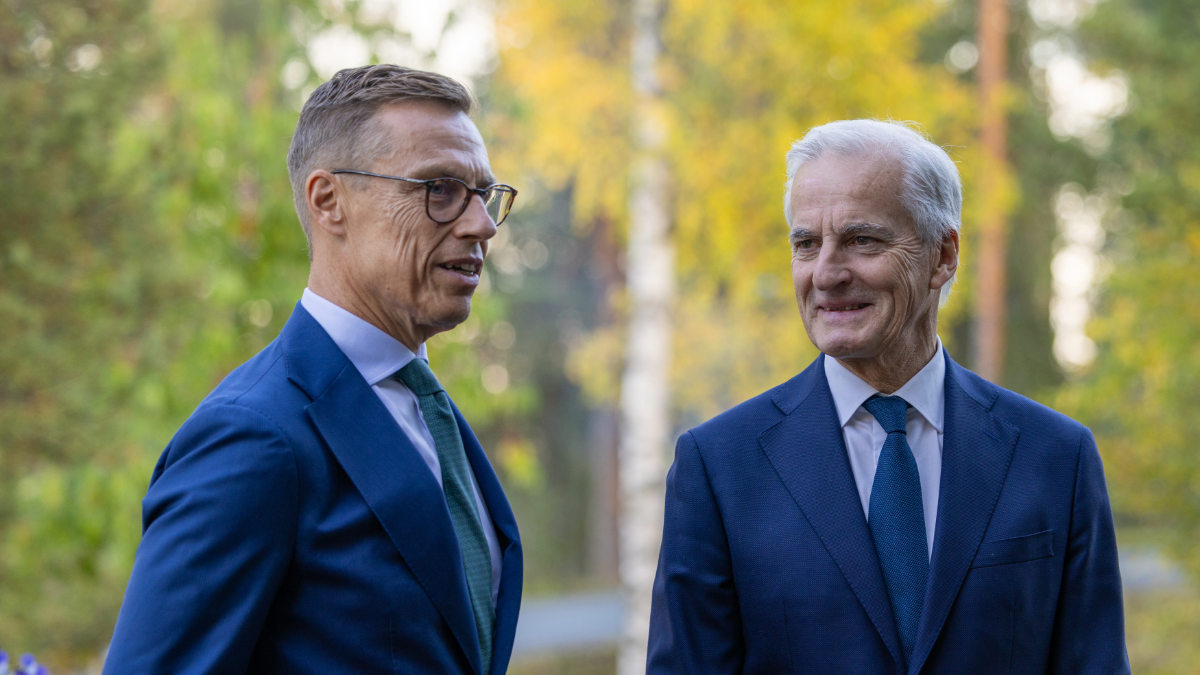
Finland President Alexander Stubb and Norway Prime Minister Jonas Gahr Støre in Rovaniemi on September 13, 2026. Photo: Katja Säilä / Finnish Government
Last month, leaders from a mostly European coalition of more than 30 countries signed a call led by the president of Finland and the prime minister of Norway for stronger controls on frontier AI. The document advocates for mandatory pre-deployment testing and independent evaluation, common standards, incident reporting, access to scientific expertise and trusted evaluation. It also proposes exploring a new international institution that could set standards, enable verification and convene states when capability thresholds are crossed. The first part is essential; the second deserves more thought.
Today, too few institutions have the technical capacity to independently understand, test and challenge frontier AI. At the same time, a small number of companies control much of the compute, capital, expertise and access to the most advanced systems. Governments therefore risk becoming dependent on the companies they are trying to regulate for the evidence needed to regulate them.
The answer should be to build capability from the bottom up.
The Internet provides an important lesson because its global reach was built alongside a system of distributed governance. The Internet did not develop around a single institution with authority over the entire network. Different organizations took responsibility for different functions and were connected through common standards, protocols and coordination mechanisms. The Internet Engineering Task Force (IETF) developed the technical standards that allow different networks and systems to interoperate. The Regional Internet Registries coordinate Internet number resources within their regions. The Internet Corporation for Assigned Names and Numbers (ICANN) coordinates critical identifiers while working with the technical community and the regional registries. None of these organizations runs the Internet. Their roles are narrower, and their effectiveness comes partly from the fact that they operate within a wider system of distributed technical responsibility.
This architecture was not designed once and imposed from above; it evolved as the network evolved. Problems created new institutions, practices and coordination mechanisms; existing institutions adapted; and technical expertise remained distributed. That did not eliminate politics or conflict. It did, however, prevent the governance of a global network from becoming dependent on a single center of authority or expertise.
The experience of Internet security makes the lesson even clearer. After the 1988 Morris worm disrupted large parts of the Internet, the initial response was fragmented and uncoordinated. The CERT Coordination Center was established, but it did not become a global cybersecurity authority. Instead, incident-response teams proliferated around different networks, sectors and countries. The creation of the Forum of Incident Response and Security Teams, or FIRST, in 1990 provided a mechanism for those teams to exchange information and coordinate across borders. The model was simple: build technical capability close to where problems occur, then connect that capability.
That approach became particularly important because one network’s security problem is every network’s security problem. A vulnerability discovered in one network can affect thousands of others. The solution was not to put every incident under one institution but to ensure that more institutions could identify, investigate and respond to problems while having mechanisms to share what they learned. FIRST today brings together government, commercial and academic incident-response teams around precisely that principle.
The lesson for AI is not to recreate the IETF, ICANN or CERTs. AI is a very different technology and has a far more concentrated architecture. The lesson is institutional: when a global system is too complex and distributed to be governed effectively from one center, build capability where it is needed and connect it through common processes.
AI currently has almost the opposite problem. Its technical infrastructure is highly concentrated, while its independent governance capacity is still thin. This is where the emerging network of AI safety, security and evaluation institutes matters as these institutes can provide the capacity governments increasingly need: testing models, evaluating risks, investigating incidents, developing benchmarks and challenging industry claims. International cooperation can then make their work comparable and useful beyond their own borders.
Not every country will need a frontier-model laboratory. But a country should be able to develop expertise relevant to how AI will actually be used within its own context. A researcher in Nairobi may identify risks involving language or public-sector applications that an evaluator in Silicon Valley misses. An institution in New Delhi may understand deployment conditions that are invisible to a European laboratory. A national or regional evaluation center can assess not only whether a system is safe in the abstract, but whether it is appropriate for the institutions, populations and infrastructure in which it will operate.
This also speaks to the claims over digital sovereignty. In today’s technological environment, digital sovereignty should not be all about technological self-sufficiency or building every component domestically. It should also be about having the capacity to determine how AI is used within a country’s own legal, economic and social context; to understand its potential benefits and harms; and to make informed decisions about the risks it is prepared to accept.
That requires expertise. A government cannot meaningfully determine how AI should be used if it has to rely entirely on the companies developing it, or on assessments produced somewhere else. The answer is therefore not to centralize expertise but to distribute it and make it interoperable. An evaluation conducted in London should be comparable with one conducted in Nairobi. A benchmark developed in Singapore should be reproducible elsewhere. A vulnerability discovered in one country should not remain there. Methods, evidence, incident reports and lessons should move across borders.
This requires common standards for evaluation, security, data handling and reporting; trusted mechanisms for sharing sensitive information; accreditation so that institutions can demonstrate the technical and security capacity to handle frontier systems; and pathways to controlled model access. This is where a multistakeholder approach can add value to AI governance, by connecting the different capabilities required to test, understand and govern these systems.
Governments can set rules and accountability requirements; companies can provide access and technical information; researchers and independent institutes can test and challenge systems; and civil society can bring perspectives on rights, harms and real-world impacts. The objective is not to give every actor an equal seat at the table, but to ensure that no single actor controls the knowledge needed to govern AI.
The emerging network of AI safety and evaluation institutes is therefore an important part of this architecture. It provides something that another global authority cannot provide on its own: independent technical capacity on the ground. Governments still have a central role in establishing obligations for testing, evaluation, verification, reporting and early warning, as well as setting requirements for access, security and accountability. They should also invest in national and regional expertise. But they do not need to own all of that expertise. International institutions can establish common expectations and facilitate political coordination, while independent institutes provide the technical capacity to determine whether those expectations are being met. The goal should be a system in which expertise is distributed, connected and capable of challenging both governments and companies when necessary.
The priority should be to strengthen the network that can make those rules work: institutes that can independently scrutinize AI, wherever they are needed, and mechanisms that allow what they learn to be shared elsewhere.
The Internet did not become governable because someone eventually found the right institution to put in charge of it. It became governable because technical responsibility was distributed and the people exercising it learned how to coordinate. AI governance should learn the same lesson.
Authors